Grey box
Signed in, like a real user. Or a stolen account.
- Public APIs
- Access control across roles
- Prompt injection and LLM leaks
Pentests for AI startups that ship fast and have no security team yet.
Signed scope first. Retest included.
One tenant can read another tenant's chat history
GET /api/v1/conversations?tenant=acme-b
Authorization: Bearer <token for acme-a>

200 OK  [ 42 conversations ]
About
We're offensive security and AI engineers. We test what you actually run: your API, your roles, your LLM features. You get findings your engineers can fix, and a retest once they have.
Services
Pick how much we know going in.
Signed in, like a real user. Or a stolen account.
Nothing but your domain, like an outside attacker.
People
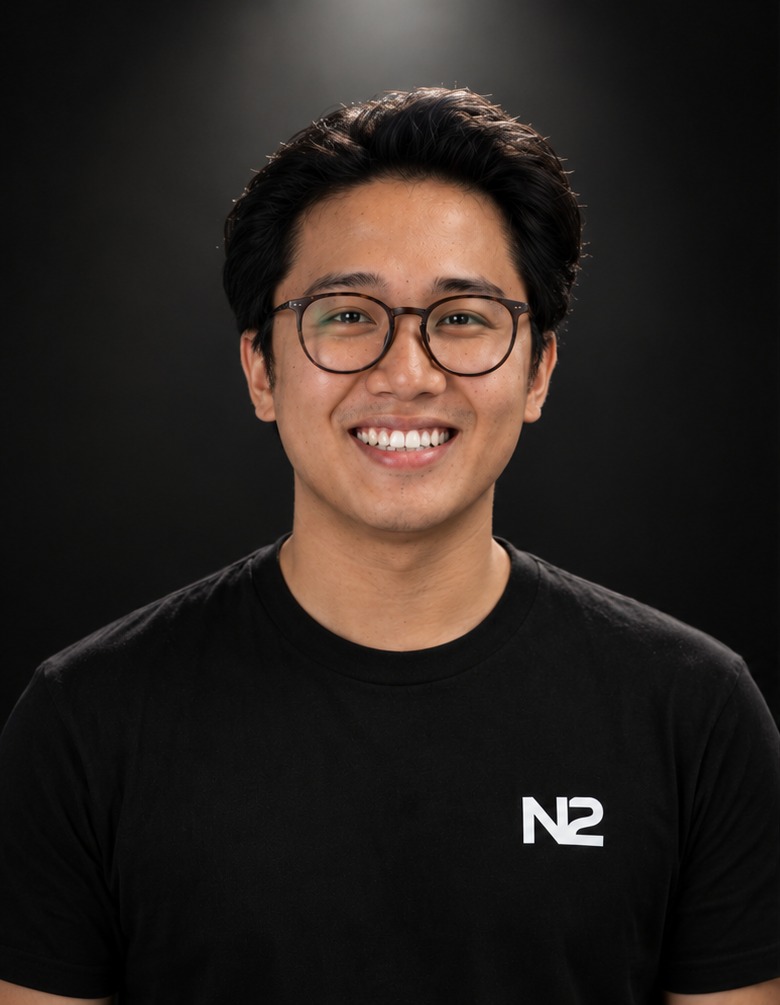
Max Ngo
Offensive Security Engineer, NAB
Ex Canva · BSc, Swinburne
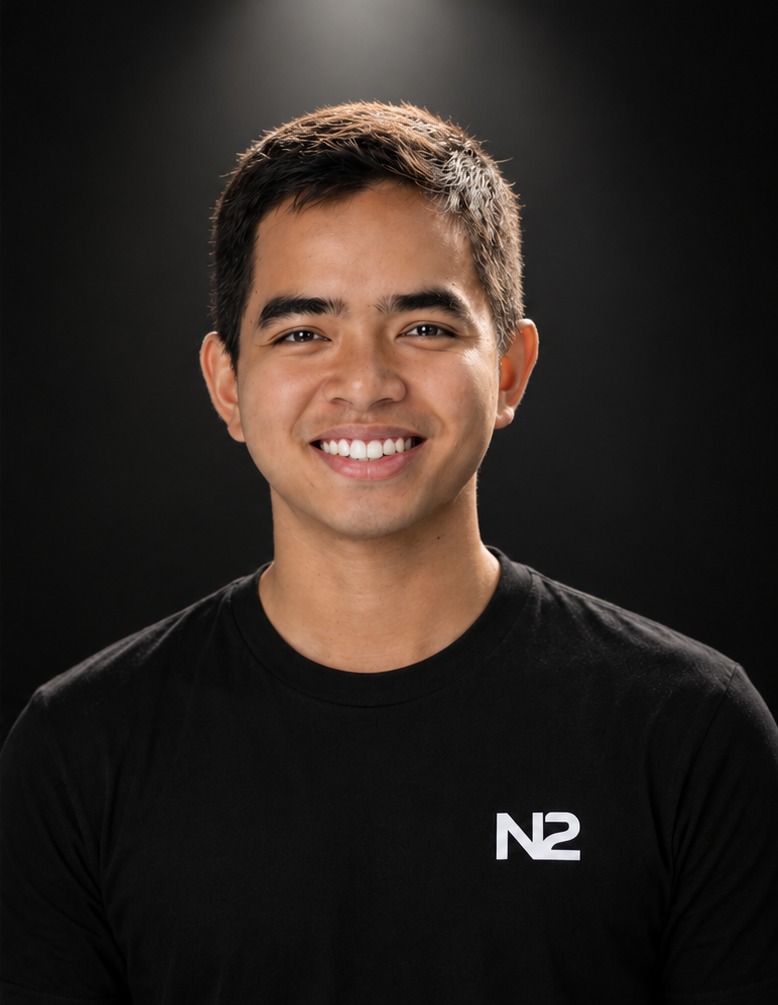
Duc Nguyen
AI Engineer
Ex Celonis · MSc, TUM
Blog
Prompt injection gets the headlines. The leaks come from the plumbing behind the chat box.
IDs in URLs, trusted headers, unchecked bulk endpoints.
Test accounts, a signed scope and who to call when we find something.
A 30-minute call to agree on scope. Nothing starts without your sign-off.